
By Anjali Sharma
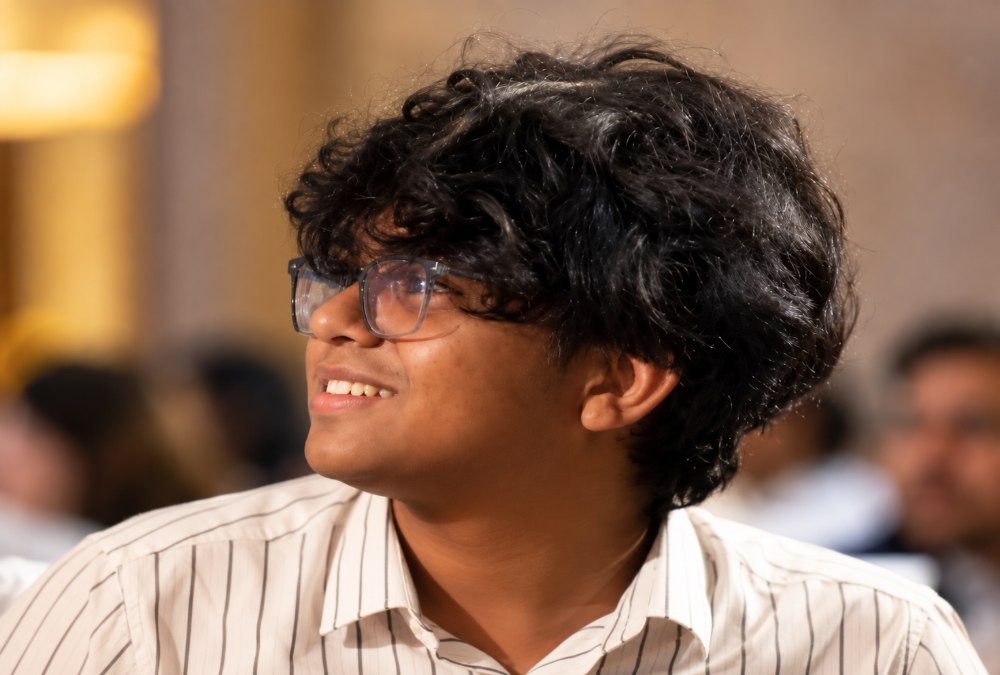
WASHINGTON – US Department of Justice (DoJ)’s cybersecurity Hall of Fame on Saturday has named 19-year-old cybersecurity researcher, Nisarga Adhikary, who found major flaws in the CBSE’s Online Submission of Marks portal
Nisarga Adhikary, 19-year-old cybersecurity researcher has been named in the US DoJ’s cybersecurity Hall of Fame after reporting a critical vulnerability.
Nisarga said the acknowledgement came after he discovered a critical vulnerability in one of the department’s major law enforcement systems.
He told India Today Tech that the issue was reported to the DoJ about a week ago and was fixed shortly after the department validated his report.
“I found a critical vulnerability in one of their largest law enforcement systems,” Nisarga told India Today Tech.
He did not disclose details about the vulnerability or identify the affected system.
Nisarga Adhikary said the DoJ verified and fixed the issue within a week of receiving his report.
“I reported the vulnerability roughly a week ago, they validated and patched this within a week and credited me on their Hall of Fame/acknowledgements page,” he said.
Nisarga also shared a screenshot of the DoJ’s acknowledgements page on X.
The page lists researchers who have responsibly reported valid security vulnerabilities to the department.
He said he discovered the flaw while browsing the DoJ website and using scripts that he had created himself. Such custom scripts can help cybersecurity researchers identify possible weaknesses in websites and computer systems.
Nisarga clarified that he did not receive any payment for reporting the vulnerability to the DoJ.
He also said the DoJ issue was not the only vulnerability he had reported to US authorities.
According to him, he found vulnerability in a US Department of Defense or military system and reported it to the authorities.
“I found vulnerability in the US Department of Defense/US military system,” he said. “I reported it and after validation, they found it was valid. Remediation is still under way though.”
The remediation refers to the process of investigating and fixing a reported security vulnerability.
Nisarga has also received a “Thanks” from the US Department of Defense on HackerOne, a platform commonly used to report cybersecurity vulnerabilities.
He said he has identified and reported other security issues to US authorities as well, added that his curiosity helped him make these discoveries.
Nisarga came into the spotlight in May after reported security flaws in the CBSE’s Online Submission of Marks portal.
He found that answer sheets of students could be accessed online without proper verification.
The discovery raised concerns about the security of students’ examination data on the portal.
Nisarga was hired as an Open-Source Intelligence and Threat Intelligence Engineer at C3iHub, IIT Kanpur after the CBSE incident.
